CISM and CISSP the Best Cybersecurity Cert for Salary

Cybersecurity has become one of the most rewarding career paths in Nigeria. As digital transformation continues across industries, organizations are investing heavily in protecting their systems, networks, and sensitive information. Because of this growing demand, cybersecurity certifications have become valuable assets for professionals seeking career advancement.

Among the certifications that stand out globally are CISM (Certified Information Security Manager) and CISSP (Certified Information Systems Security Professional). Both credentials are highly respected. However, each certification serves a different purpose. Consequently, many Nigerian professionals wonder which option offers better salary prospects and career opportunities.

If you are considering a cybersecurity certification, understanding the differences between CISM and CISSP can help you make an informed decision.
What Is CISM?

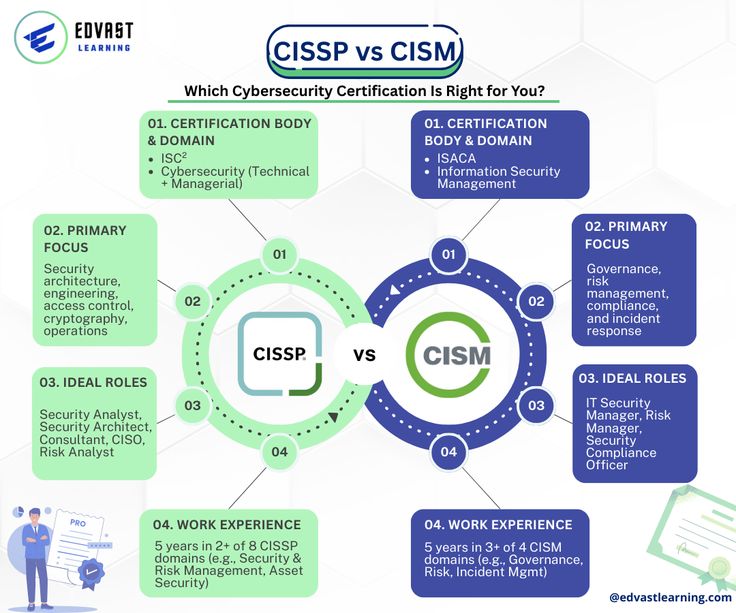
CISM is a professional certification offered by ISACA. Rather than focusing heavily on technical security operations, this certification emphasizes security governance, risk management, and leadership.

For that reason, CISM is often preferred by professionals who want to move into management positions. In other words, it prepares individuals to align cybersecurity initiatives with business objectives.

Topics Covered in CISM

The certification focuses on:

  • Information Security Governance
  • Information Risk Management
  • Information Security Programs
  • Incident Management

As a result, CISM certified professionals are equipped to manage security strategies and oversee organizational cybersecurity efforts.

What Is CISSP?

Unlike CISM, CISSP provides a broader understanding of cybersecurity concepts and practices. This certification is offered by ISC2 and is recognized by employers around the world.

Not only does CISSP cover management principles, but it also explores technical cybersecurity domains. Therefore, it is often viewed as one of the most comprehensive certifications in the industry.

Core CISSP Domains

Professionals preparing for CISSP study:

  • Security and Risk Management
  • Asset Security
  • Security Architecture and Engineering
  • Communication and Network Security
  • Identity and Access Management
  • Security Assessment and Testing
  • Security Operations
  • Software Development Security

Because these domains cover a wide range of topics, CISSP holders can pursue numerous cybersecurity career paths.

Comparing CISM and CISSP

Although both certifications are respected globally, several distinctions set them apart.

Feature CISM CISSP
Main Focus Security Management Technical and Strategic Security
Issuing Organization ISACA ISC2
Career Direction Leadership and Governance Technical and Leadership Roles
Target Audience Managers and Leaders Security Professionals
Scope Specialized Management Broad Cybersecurity Knowledge

While CISM concentrates on managing security programs, CISSP delivers a broader understanding of cybersecurity technologies and frameworks. As such, the choice often depends on your professional interests.

Which Certification Pays More in Nigeria?

Salary remains one of the most important considerations when pursuing a certification. Nevertheless, earnings are influenced by multiple factors, including years of experience, industry sector, job responsibilities, and employer size.

Even so, both certifications can lead to lucrative careers.

CISSP Salary Expectations

Many employers view CISSP as proof of advanced cybersecurity expertise. Consequently, certified professionals often qualify for high-level technical and consulting roles.

Estimated annual salaries include:

  • Entry to Mid-Level Professionals: ₦8 million – ₦15 million
  • Senior Security Specialists: ₦15 million – ₦30 million
  • Security Architects and Executives: ₦30 million and above

Furthermore, multinational corporations frequently prioritize CISSP certified candidates when recruiting cybersecurity experts.

CISM Salary Expectations

On the management side, CISM holders are often entrusted with strategic security responsibilities. Therefore, their compensation packages can be equally attractive.

Estimated annual salaries include:

  • Information Security Managers: ₦10 million – ₦20 million
  • Risk Management Professionals: ₦12 million – ₦25 million
  • Senior Cybersecurity Executives: ₦20 million and above

In many cases, experienced CISM professionals earn salaries that rival or exceed those of CISSP holders. Ultimately, leadership responsibilities tend to command higher compensation.

Industry Demand Across Nigeria

Today, cybersecurity skills are needed in nearly every sector. Meanwhile, organizations continue to face evolving cyber threats. As a consequence, demand for certified professionals remains strong.

Industries Seeking CISM Professionals

  • Banking and Finance
  • Telecommunications
  • FinTech Companies
  • Government Institutions
  • Oil and Gas Organizations

Industries Seeking CISSP Professionals

  • Technology Companies
  • Cybersecurity Firms
  • Cloud Service Providers
  • Financial Institutions
  • Consulting Organizations

Moreover, the expansion of digital services throughout Nigeria has created additional opportunities for cybersecurity experts.

Which Certification Is Right for You?

Before choosing a certification, consider your long-term career goals.

If you aspire to lead teams, manage risk, and influence business decisions, CISM may be the better option.

By contrast, CISSP could be ideal if you enjoy technical security challenges and want expertise across multiple cybersecurity disciplines.

Another factor worth considering is future growth. Many professionals start with one certification and later obtain the other. Consequently, they become qualified for both technical and executive positions.

Why Study at Port Harcourt Data School?

Achieving certification success requires quality training and expert guidance. Fortunately, Port Harcourt Data School provides both.

Recognized as one of Africa’s leading technology training institutions, Port Harcourt Data School offers practical cybersecurity education designed to prepare students for globally recognized certifications.

Students benefit from:

  • Industry experienced instructors
  • Practical cybersecurity laboratories
  • Exam focused preparation
  • Career mentoring and support
  • Flexible learning schedules

Additionally, learners gain hands on experience that helps them perform confidently in professional environments.

CONCLUSION

Without question, both CISM and CISSP can significantly increase your earning potential in Nigeria. On one hand, CISSP opens doors to advanced technical and consulting roles. On the other hand, CISM positions professionals for leadership and management opportunities.

Therefore, neither certification is universally better than the other. Instead, the ideal choice depends on your career aspirations, interests, and professional background.

Regardless of the path you choose, investing in cybersecurity education can transform your career. More importantly, receiving quality training from Port Harcourt Data School can provide the knowledge, practical skills, and confidence needed to achieve certification success and secure high-paying cybersecurity positions.

For official certification details, visit ISC2 Certifications.
CISSP Exam the Best Way to Pass in Nigeria

The Certified Information Systems Security Professional (CISSP) certification is one of the most respected cybersecurity credentials in the world. Today, cybersecurity professionals across various industries pursue this certification because it demonstrates advanced knowledge of information security. Moreover, many employers prefer candidates who possess globally recognized certifications such as CISSP.

For Nigerian professionals, obtaining the CISSP certification can significantly improve career opportunities. In addition, it can increase earning potential and create pathways to leadership positions in cybersecurity. Therefore, understanding how to prepare effectively for the exam is essential.

In this article, you will learn about the CISSP exam, discover a practical study plan, and explore proven tips that can help you pass the examination successfully.

What Is the CISSP Certification?

The CISSP certification is offered by ISC², a globally recognized cybersecurity organization. Specifically, the certification validates a professional’s ability to design, implement, and manage enterprise security programs.

Furthermore, the CISSP exam covers eight important cybersecurity domains. These domains include:

  • Security and Risk Management
  • Asset Security
  • Security Architecture and Engineering
  • Communication and Network Security
  • Identity and Access Management (IAM)
  • Security Assessment and Testing
  • Security Operations
  • Software Development Security

Additionally, candidates are encouraged to understand how these domains work together in real world security environments.

For more information, visit the official CISSP certification page at https://www.isc2.org/certifications.

Why CISSP Is Valuable for Nigerian Professionals

Cybersecurity threats continue to evolve across Nigeria and around the world. As a result, organizations are investing more resources in protecting their digital assets. Consequently, the demand for qualified cybersecurity professionals has increased significantly.

By earning the CISSP certification, professionals can:

  • Gain international recognition
  • Qualify for senior cybersecurity roles
  • Increase professional credibility
  • Improve security management skills
  • Access global job opportunities

Moreover, many multinational organizations consider CISSP a preferred qualification for leadership positions. Therefore, obtaining the certification can provide a competitive advantage in the job market.

Understanding the CISSP Exam

Before beginning your preparation, it is important to understand the structure of the exam. Although the CISSP exam contains technical concepts, it also emphasizes risk management and business decision making.

Therefore, candidates must learn to think from both technical and managerial perspectives. In other words, success requires more than memorizing definitions. Instead, you must understand how security principles are applied in practical situations.

Furthermore, many exam questions are scenario-based. As a result, critical thinking and analytical skills become extremely important.

A CISSP Study Plan

Learn the CISSP Domains

First, spend time understanding the eight CISSP domains. During this phase, focus on gaining a broad understanding of cybersecurity concepts.

Additionally, identify areas where you already have experience and areas that require more attention.

Your objectives should include:

  • Reviewing exam objectives
  • Creating a study timetable
  • Understanding key concepts
  • Gathering study resources

As a result, you will establish a strong foundation for future learning.

Study Core Concepts in Depth

Next, begin a deeper study of each domain. For example, you may choose to study two domains each week.

Meanwhile, take detailed notes and summarize important concepts in your own words. Furthermore, watch educational videos and participate in cybersecurity discussions whenever possible.

By doing so, you will improve both understanding and retention.

Practice Questions and Revision

Once you have completed the main study phase, focus on revision and practice questions.

Specifically, you should:

  • Complete daily practice tests
  • Review incorrect answers
  • Revisit weak topics
  • Strengthen understanding of security frameworks

Consequently, you will become more familiar with the exam format and question style.

Moreover, regular practice helps reduce anxiety before the actual examination.

Mock Exams and Final Preparation

Finally, dedicate the last month to full exam simulations.

During this stage:

  • Take timed mock examinations
  • Improve time management skills
  • Review summary notes
  • Focus on weak areas

Furthermore, avoid overwhelming yourself with entirely new topics. Instead, concentrate on reinforcing existing knowledge.

As a result, you will enter the exam with greater confidence.

Essential CISSP Exam Tips

Follow a Consistent Study Schedule

Consistency is one of the most important factors in exam preparation. Instead of studying occasionally, create a routine that allows you to learn regularly.

For example:

  • Study 1–2 hours on weekdays
  • Study 3–4 hours on weekends

Consequently, you will retain information more effectively.

Focus on Understanding Rather Than Memorization

Many candidates make the mistake of memorizing information without understanding it. However, CISSP questions often test practical decision-making.

Therefore, focus on understanding:

  • Why security controls are implemented
  • How risks are managed
  • When security policies should be applied

As a result, you will perform better in scenario-based questions.

Use Multiple Study Resources

Although textbooks are valuable, they should not be your only resource.

In addition to study guides, consider:

  • Video courses
  • Practice exams
  • Security blogs
  • Online communities
  • Training programs

Furthermore, using different learning methods helps reinforce knowledge from multiple perspectives.

Practice Questions Every Day

Practice questions are extremely beneficial because they reveal weaknesses in your understanding.

Moreover, they improve familiarity with exam wording and structure.

Therefore, make daily practice a key part of your preparation strategy.

Think Like a Security Leader

One unique feature of the CISSP exam is its management-oriented approach.

Consequently, candidates should focus on:

  • Risk reduction
  • Business objectives
  • Security governance
  • Organizational impact

In many cases, the best answer is not the most technical solution but the one that best supports business goals.

Join a Study Community

Studying alone can sometimes become difficult. Therefore, joining a study group can provide additional motivation and support.

Furthermore, discussing cybersecurity topics with others can help clarify difficult concepts.

As a result, you’re learning experience becomes more effective and engaging.

Common Mistakes to Avoid

While preparing for the CISSP exam, avoid the following mistakes:

  • Starting preparation too late
  • Ignoring practice exams
  • Memorizing without understanding
  • Neglecting difficult domains
  • Studying inconsistently

Unfortunately, these mistakes often contribute to exam failure. However, proper planning can help you avoid them.

Why Choose Port Harcourt Data School for CISSP Preparation?

Preparing for the CISSP exam can be challenging. Therefore, choosing the right training institution is extremely important.

Port Harcourt Data School has established itself as one of the leading technology training institutions in Africa. Moreover, the school is committed to helping students develop practical cybersecurity skills that align with industry requirements.

Students benefit from:

  • Experienced cybersecurity instructors
  • Hands on practical training
  • Career focused mentorship
  • Industry relevant curriculum
  • Supportive learning environment

Furthermore, learners receive guidance that helps them prepare for globally recognized certifications and real-world cybersecurity challenges.

Consequently, graduates are better positioned for success in the cybersecurity industry.

Conclusion

The CISSP certification remains one of the most valuable credentials for cybersecurity professionals. Although the exam can be challenging, success is achievable with proper preparation and dedication.

By following a structured study plan, practicing consistently, and focusing on understanding security concepts, Nigerian candidates can improve their chances of passing the exam.

Most importantly, choose quality training and remain committed to your goals. Ultimately, with the right preparation and support from Port Harcourt Data School, you can earn your CISSP certification and advance your cybersecurity career to the next level.

Is CompTIA Security+ Good for Cybersecurity Jobs?

CompTIA Security+ has become one of the most sought-after cybersecurity certifications for professionals who want to build a successful career in information security. As cyber threats continue to increase across the globe, organizations are actively looking for skilled individuals who can protect their systems, networks, and sensitive data. Therefore, the demand for cybersecurity professionals continues to grow in Nigeria and beyond.

In today’s digital economy, businesses, government agencies, financial institutions, and technology companies rely heavily on cybersecurity to protect their operations. Consequently, certifications such as CompTIA Security+ are being recognized as valuable credentials that validate essential cybersecurity knowledge and practical skills.

Many Nigerian professionals, students, and IT practitioners are now considering CompTIA Security+ as a pathway to better career opportunities and professional growth. However, an important question is often asked: Is CompTIA Security+ worth the investment?

The answer is yes for many aspiring cybersecurity professionals. CompTIA Security+ provides a strong foundation in cybersecurity, enhances employability, and prepares candidates for various security-related roles. In this article, we will explore the benefits of CompTIA Security+, the career opportunities it offers, and why Port Harcourt Data School is regarded as one of the best technology training institutions in Africa for cybersecurity education.

What Is CompTIA Security+?

CompTIA Security+ is a globally recognized cybersecurity certification offered by CompTIA. It validates the essential knowledge and skills required to secure networks, systems, and digital assets.

The certification covers key areas such as:

  • Network Security
  • Threat Management
  • Risk Assessment
  • Security Operations
  • Identity and Access Management
  • Cryptography
  • Incident Response
  • Governance and Compliance

Many organizations recognize Security+ because it focuses on practical cybersecurity concepts rather than vendor-specific technologies. As a result, certified professionals can apply their knowledge across different industries and platforms.

For additional information, visit the official CompTIA website: www.comptia.org.

Why Do Employers Value CompTIA Security+?

Employers value Security+ because it demonstrates a candidate’s understanding of cybersecurity fundamentals. Furthermore, the certification confirms that an individual can identify risks, respond to threats, and implement security controls.

Unlike some certifications that focus on a single technology, Security+ teaches broad cybersecurity principles. Therefore, employers can trust that certified professionals possess versatile security knowledge.

Additionally, many government agencies and multinational organizations recognize Security+ as a respected industry credential.

Benefits of CompTIA Security+ for Nigerian Professionals

Increased Job Opportunities

The cybersecurity industry continues to expand across Nigeria. As more organizations digitize their operations, they require qualified professionals to protect their systems.

With a Security+ certification, you can strengthen your resume and improve your chances of securing cybersecurity-related roles.

Potential job positions include:

  • Cybersecurity Analyst
  • SOC Analyst
  • Security Administrator
  • Security Specialist
  • Information Security Officer
  • Security Consultant

Consequently, certified professionals often gain access to a wider range of employment opportunities.

Global Recognition

CompTIA Security+ enjoys worldwide recognition. Therefore, Nigerian professionals can use the certification to pursue both local and international opportunities.

Many employers around the world accept Security+ as proof of cybersecurity competence. As a result, remote work opportunities may also become more accessible.

Strong Cybersecurity Foundation

Security+ introduces learners to essential cybersecurity concepts. It helps students understand threats, vulnerabilities, risk management, and security best practices.

Furthermore, the certification builds a foundation for advanced cybersecurity studies.

After earning Security+, professionals often pursue certifications such as:

  • CySA+
  • PenTest+
  • CASP+
  • CEH
  • CISSP

Consequently, long-term career growth becomes easier to achieve.

Improved Professional Credibility

When you earn a recognized certification, employers often view you as a more serious and committed professional.

Additionally, certification demonstrates your willingness to invest in continuous learning and professional development.

As a result, your credibility within the technology industry may increase significantly.

Better Earning Potential

Many organizations reward certified professionals with competitive salaries. Although experience remains important, certifications can strengthen salary negotiations.

Furthermore, employers often use certifications as part of their promotion and advancement criteria.

Therefore, Security+ can contribute to long-term financial growth.

Is CompTIA Security+ Good for Beginners?

Yes, Security+ serves as an excellent starting point for beginners.

Students, recent graduates, IT support staff, and career changers can all benefit from the certification. Although some technical knowledge helps, beginners can successfully prepare for Security+ through structured training programs.

The certification introduces cybersecurity concepts in a clear and organized manner. Therefore, learners can gradually build confidence while developing practical skills.

Challenges to Consider

While Security+ offers numerous advantages, professionals should also consider a few challenges.

Certification Costs

Candidates must pay for training materials and examination fees. Therefore, proper preparation becomes important to maximize the value of the investment.

Ongoing Learning

Cybersecurity evolves rapidly. New threats emerge regularly, and security technologies continue to change.

Consequently, professionals must continue learning even after earning the certification.

Practical Experience Matters

Although employers respect certifications, they also value practical experience.

Therefore, students should combine certification preparation with hands-on training and real-world projects. This approach helps them develop stronger technical skills and workplace readiness.

Why Choose Port Harcourt Data School?

Your choice of training institution can significantly influence your learning experience and career success. Therefore, selecting a reputable institution is essential.

Port Harcourt Data School has built a strong reputation for delivering practical technology education across Africa. The institution focuses on helping students develop industry relevant skills that employers demand.

Experienced Instructors

Industry professionals lead the training programs and share practical cybersecurity knowledge with students.

Hands On Learning

Students participate in practical exercises, cybersecurity labs, and real-world scenarios. As a result, they gain valuable experience that complements theoretical learning.

Industry Focused Curriculum

The school designs its curriculum to align with current cybersecurity trends and employer expectations.

Therefore, students can prepare effectively for certification examinations and professional careers.

Career Support

Port Harcourt Data School also provides career guidance, interview preparation, and professional development support.

Consequently, graduates can approach the job market with greater confidence.

Is CompTIA Security+ Worth It?

CompTIA Security+ remains one of the most valuable entry level cybersecurity certifications available today. It helps professionals build foundational cybersecurity skills, improve their employability, and prepare for advanced certifications.

Furthermore, the certification opens doors to local and international career opportunities. While dedication and continuous learning remain necessary, the benefits often outweigh the costs.

For Nigerian professionals who want to enter cybersecurity or strengthen their existing IT careers, Security+ represents a smart investment.

When combined with practical training from Port Harcourt Data School, the certification can help learners build the knowledge, confidence, and experience needed to succeed in today’s competitive cybersecurity industry.

Multi-Cloud Security: How To Lower Risk On AWS AND GCP

Multi-cloud security has become increasingly important because many businesses now use more than one cloud provider to run applications, store data, and support business operations. As organizations adopt AWS, Microsoft Azure, and Google Cloud Platform (GCP) simultaneously, managing security becomes more challenging. Therefore, companies need a strong multi-cloud security strategy to reduce risks and maintain visibility across all environments.

Imagine a growing business using AWS for application hosting, Azure for collaboration services, and Google Cloud for data analytics. Meanwhile, each platform has different security settings, access controls, and monitoring tools. Consequently, a security gap in one environment could expose sensitive business information and create costly problems.

Naturally, one important question appears:

How can organizations manage security effectively across multiple cloud platforms?

The answer begins with understanding multi-cloud security principles and implementing consistent protection measures.

If terms such as cloud governance, identity management, workload protection, and security monitoring sound complicated, do not worry. This guide explains everything in simple language for business owners, startup founders, IT managers, and technology professionals.

What Is Multi-Cloud Security?

Multi-cloud security refers to the strategies, technologies, and processes used to protect systems, applications, and data across multiple cloud providers.

Instead of relying on a single cloud vendor, organizations distribute workloads across different platforms.

Consequently, businesses gain flexibility and resilience.

However, they also face additional security challenges.

Therefore, effective security management becomes essential.

Why Businesses Use Multi-Cloud Environments

Many organizations adopt multi-cloud strategies for several reasons.

Firstly, they reduce dependence on a single provider.

Secondly, they improve business continuity.

Thirdly, they take advantage of specialized services offered by different platforms.

Additionally, companies can optimize costs and performance.

As a result, multi-cloud adoption continues growing worldwide.

Common Multi-Cloud Security Risks

Inconsistent Security Policies

Each cloud platform offers unique security controls.

Consequently, businesses may struggle to maintain consistent security standards.

Visibility Challenges

Security teams often manage multiple dashboards and monitoring systems.

Therefore, identifying threats becomes more difficult.

Misconfigured Cloud Resources

Configuration mistakes remain one of the leading causes of cloud security incidents.

As a result, sensitive information may become exposed.

Identity and Access Management Issues

Managing user permissions across multiple environments can become complex.

Consequently, excessive privileges may create security risks.

Compliance Challenges

Organizations must comply with regulations and industry standards.

Therefore, maintaining compliance across several cloud providers requires careful planning.

Key Components of a Multi-Cloud Security Strategy

Centralized Identity Management

Businesses should establish unified identity and access controls.

Consequently, administrators can manage permissions more efficiently.

Moreover, centralized authentication reduces unauthorized access risks.

Continuous Security Monitoring

Organizations must monitor all cloud environments continuously.

Therefore, suspicious activity can be detected quickly.

Additionally, real-time monitoring improves incident response.

Data Encryption

Sensitive information should remain encrypted both in storage and during transmission.

As a result, attackers face greater difficulty accessing valuable data.

Security Automation

Automation helps businesses identify vulnerabilities and enforce security policies.

Consequently, teams can focus on higher-priority security tasks.

Regular Security Audits

Periodic audits help organizations identify weaknesses.

Therefore, businesses can address risks before attackers exploit them.

AWS Security Best Practices

AWS provides numerous security tools for protecting cloud resources.

For example:

  • Identity and Access Management (IAM)
  • Security Hub
  • GuardDuty
  • CloudTrail
  • Key Management Service (KMS)

Consequently, organizations gain strong visibility and protection.

Azure Security Best Practices

Microsoft Azure offers several security capabilities.

Examples include:

  • Microsoft Defender for Cloud
  • Azure Active Directory
  • Azure Security Center
  • Key Vault

Therefore, businesses can strengthen cloud protection across Azure environments.

Google Cloud Security Best Practices

Google Cloud Platform focuses heavily on infrastructure security.

Popular security services include:

  • Security Command Center
  • Identity and Access Management
  • Cloud Key Management
  • Cloud Armor

As a result, organizations benefit from advanced cloud protection.

Benefits of Strong Multi-Cloud Security

Organizations gain several advantages when they implement effective security strategies.

Firstly, they improve risk management.

Secondly, they enhance business continuity.

Thirdly, they strengthen regulatory compliance.

Furthermore, they improve customer trust.

Ultimately, secure cloud environments support long-term business growth.

Frequently Asked Questions

What Is Multi-Cloud Security?

Multi-cloud security involves protecting systems and data across multiple cloud providers such as AWS, Azure, and Google Cloud.

Why Do Businesses Use Multiple Cloud Providers?

Organizations use multiple providers to improve flexibility, resilience, and performance.

Is Multi-Cloud More Secure?

It can be secure when businesses implement proper security controls and governance policies.

What Is the Biggest Multi-Cloud Security Challenge?

Managing visibility and maintaining consistent security policies across different platforms remain major challenges.

Why Multi-Cloud Security Skills Matter Today

Cloud adoption continues accelerating across industries.

Therefore, employers increasingly seek professionals who understand cloud security and risk management.

Career opportunities include:

Consequently, multi-cloud expertise remains highly valuable.

Why Learners Choose Port Harcourt Data School

Many technology learners want skills that match current industry demands. Therefore, Port Harcourt Data School helps students build practical knowledge in cloud computing and cybersecurity.

Exposure to Multiple Cloud Technologies

Students gain insights into different cloud platforms rather than focusing on only one environment.

Consequently, they develop broader technical capabilities.

Project-Based Learning Approach

Learners work on practical scenarios and cloud-related projects.

Therefore, they gain experience that supports real-world problem-solving.

Industry-Relevant Technology Education

Training focuses on skills employers actively seek.

As a result, students become more competitive in the job market.

Focus on Emerging Technology Trends

Cloud computing and cybersecurity continue evolving rapidly.

Therefore, learners stay informed about modern industry developments.

Career Development Support

Students receive guidance that helps them align their learning with professional goals.

Consequently, they prepare more effectively for future opportunities.

Strengthen Your Multi-Cloud Security Strategy Today

Multi-cloud security plays a critical role in protecting modern business operations because organizations increasingly depend on AWS, Azure, and Google Cloud. Therefore, companies must implement strong security controls across all cloud environments.

Meanwhile, professionals with multi-cloud security expertise continue to enjoy growing demand in the technology industry.

If you want practical cloud computing and cybersecurity training, explore Port Harcourt Data School and begin developing future-ready skills today.

Visit: https://portharcourtdataschool.com/

If you want to really secure your cloud, it’s pretty simple: you need to see everything that’s happening, stick to a solid routine, and just keep learning as you go.

DevSecOps Explained: How To Secure Your Cloud Pipeline

DevSecOps has become a critical approach in modern software development because businesses now build and deploy applications faster using cloud pipelines, CI/CD automation, and DevOps practices. As development speed increases, security risks also increase. Therefore, organizations must integrate security into every stage of the software delivery process to protect applications, data, and infrastructure.

Imagine a startup deploying updates to production multiple times per day. Meanwhile, a hidden vulnerability enters the system during deployment without anyone noticing. Consequently, attackers exploit the weakness and gain access to sensitive customer data, causing financial and reputational damage.

Naturally, one important question appears:

How can businesses secure their cloud pipeline without slowing down development speed?

The answer lies in DevSecOps.

If terms like CI/CD, pipeline, automation, vulnerability scanning, and infrastructure as code sound complex, do not worry. This guide explains DevSecOps in simple language for business owners, developers, startups, and IT professionals.


What Is DevSecOps?

DevSecOps means integrating security into DevOps processes from the beginning of software development.

Instead of adding security at the end, teams build security into every stage of the pipeline.

Consequently, vulnerabilities are detected earlier and fixed faster.

Moreover, DevSecOps ensures that development, operations, and security teams work together.

Why DevSecOps Matters

Modern software systems change frequently.

Therefore, manual security checks cannot keep up with rapid deployments.

Additionally, attackers often target fast-moving systems because they may contain unnoticed vulnerabilities.

As a result, integrating security into the pipeline becomes essential.

Without DevSecOps, organizations risk deploying insecure code into production.

How a Cloud Pipeline Works

A cloud pipeline automates the process of building, testing, and deploying applications.

It typically includes:

  • Code development
  • Build process
  • Testing stage
  • Deployment stage
  • Monitoring stage

Consequently, developers can release updates quickly and efficiently.

However, without security integration, each stage may introduce risks.

Core Principles of DevSecOps

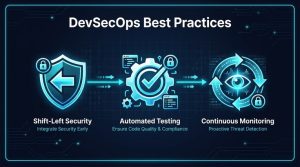
Shift Left Security

Security is applied early in the development cycle.

Therefore, issues are identified before deployment.

Automation

Security checks are automated within the pipeline.

As a result, teams reduce manual errors.

Continuous Monitoring

Systems are monitored even after deployment.

Consequently, threats are detected in real time.

Collaboration

Development, security, and operations teams work together.

Therefore, communication improves across all stages.

Key DevSecOps Practices

Secure Code Analysis

Static application security testing helps identify vulnerabilities in code.

Consequently, developers fix issues before deployment.

Dependency Scanning

External libraries are checked for security risks.

Therefore, unsafe components are avoided.

Container Security Integration

Containers are scanned before deployment.

As a result, vulnerabilities are reduced in production environments.

Infrastructure as Code Security

Configuration files are reviewed for misconfigurations.

Therefore, cloud environments remain secure.

Continuous Monitoring Tools

Security tools track system behavior in real time.

Consequently, threats are detected early.

Benefits of DevSecOps

Organizations gain several advantages when they adopt DevSecOps practices.

Firstly, they improve application security.

Secondly, they reduce production vulnerabilities.

Thirdly, they speed up incident response.

Additionally, they increase development efficiency.

Ultimately, businesses build more secure and reliable systems.

Common DevSecOps Challenges

Many organizations face challenges when adopting DevSecOps.

For example:

  • Lack of security knowledge among developers
  • Complex tool integration
  • Resistance to workflow changes
  • Limited automation experience
  • Poor communication between teams

Therefore, proper training and structured implementation become important.

DevSecOps Tools Used in Industry

Popular tools include:

  • Jenkins for CI/CD automation
  • SonarQube for code analysis
  • Snyk for vulnerability scanning
  • Docker for containerization
  • Kubernetes for orchestration

Consequently, teams can secure applications at every stage.

Frequently Asked Questions

What Is DevSecOps?

DevSecOps is the practice of integrating security into the DevOps pipeline from development to deployment.

Why Is DevSecOps Important?

It helps detect vulnerabilities early and prevents insecure applications from reaching production.

Does DevSecOps Slow Down Development?

No. Automation ensures security without reducing deployment speed.

Can Small Businesses Use DevSecOps?

Yes. Small businesses can adopt scalable DevSecOps practices using modern tools.

Why DevSecOps Skills Matter Today

Cloud development continues growing rapidly across industries.

Therefore, companies now seek professionals who understand both development and security.

Career opportunities include:

Consequently, DevSecOps skills remain highly valuable in the modern job market.

Why Learners Choose Port Harcourt Data School

Many learners struggle with DevSecOps because it combines development, operations, and security concepts. Therefore, Port Harcourt Data School provides structured learning that simplifies complex topics.

Hands-On Pipeline Practice

Students work with real CI/CD pipelines.

Consequently, they gain practical experience.

Real-World Security Integration

Learners practice adding security into development workflows.

Therefore, they understand industry expectations.

Beginner-Friendly Learning Path

Complex topics are broken into simple steps.

As a result, learners progress easily.

Career-Focused Training

Courses prepare students for DevOps and cloud security roles.

Therefore, employability increases.

Exposure to Modern Industry Tools

Students use tools commonly applied in real companies.

Consequently, they become job-ready.

Build Secure Cloud Pipeline Skills Today

DevSecOps has become essential because modern software development requires both speed and security. Therefore, businesses must integrate security into every stage of their cloud pipeline.

Meanwhile, professionals with DevSecOps skills are in high demand across global tech industries.

If you want practical DevOps and cloud security training, explore Port Harcourt Data School and start building your future-ready skills today.

Visit: https://portharcourtdataschool.com/

Ultimately, secure software delivery begins with strong collaboration, automation, and continuous learning.

Hi, How Can We Help You?
Welcome To
Portharcourt Data School

Artificial Intelligence (AI) and Robotics Programmes Are Now Available!

Enroll Now!

Thank You
100% secure website.